
Unlock top-tier solutions with Kinverg’s expert services tailored to drive your success. ISO 27001 is a widely recognized international standard that helps businesses manage their information security effectively. This standard provides a structured approach to establishing and maintaining an Information Security…
ISO 27001 in Asia Pacific (APAC)
Unlock top-tier solutions with Kinverg’s expert services tailored to drive your success. ISO 27001 in APAC: A Framework for Cyber Resilience, Not a Breach Proof Badge Cybersecurity teams across Asia-Pacific face a practical challenge: deciding which risks to address first, who…
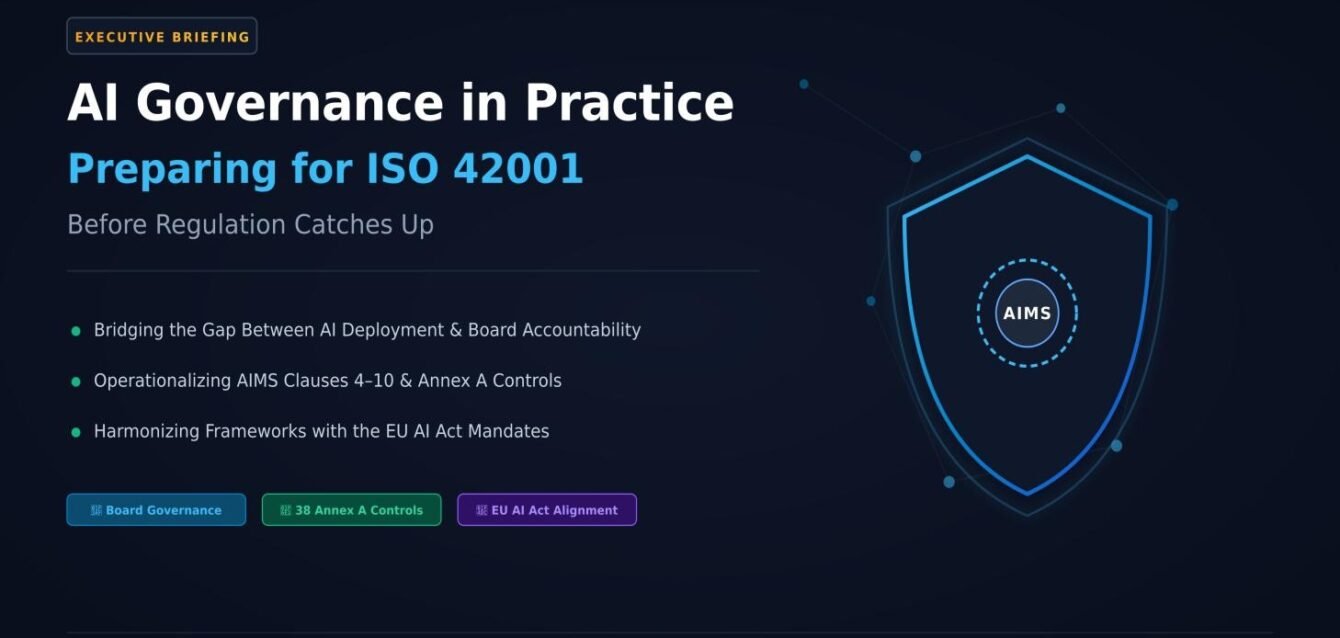
AI Governance in Practice: Preparing for ISO 42001
Unlock top-tier solutions with Kinverg’s expert services tailored to drive your success. AI Governance in Practice: Preparing for ISO 42001 Before Regulation Catches Up Every executive team is wrestling with the same uncomfortable truth. AI is being deployed faster than it…
Top 7 Compliance Gap Analysis Tools-Simplifying Compliance
Unlock top-tier solutions with Kinverg’s expert services tailored to drive your success. Top 7 Compliance Gap Analysis Tools-Simplifying Compliance In today’s rapidly evolving regulatory landscape, compliance is no longer a one-time exercise; it is a continuous process. Organizations must comply with multiple regulations such as…
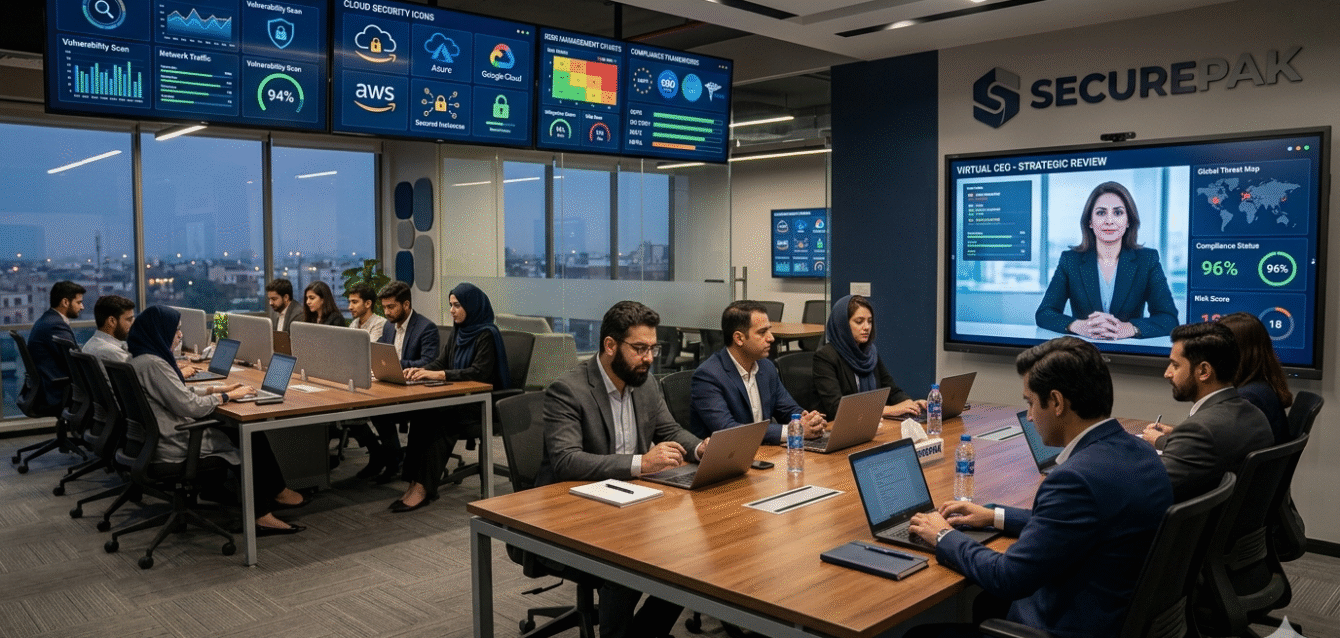
The Missing Security Leader: Why Every Growing Company in Pakistan Needs a vCISO
Pakistan’s digital economy is expanding at an unprecedented pace. From technology startups and Fintech innovators to e-commerce platforms and professional services firms, organizations are embracing cloud technologies, remote work, and digital transformation to accelerate growth. Yet as businesses scale, so do…
Cyber Shield vs ISO 27001: Where Do They Align and Where Do They Differ?
In the current hyper-connected global economy, digital transformation has introduced complex risks alongside unprecedented opportunities. For cybersecurity GRC professionals, navigating the landscape of frameworks is essential to building a resilient organization. Two critical frameworks often discussed in the Pakistani financial sector…
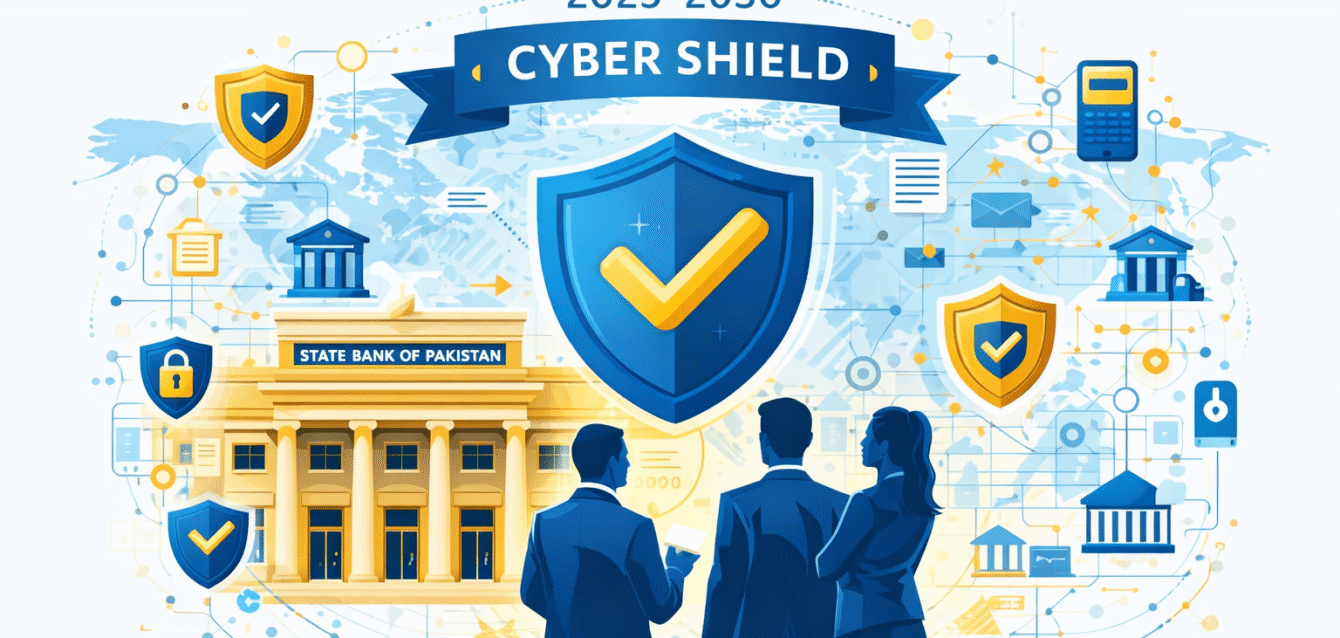
What SBP Cyber Shield Means for Banks & Fintechs in Pakistan
Pakistan’s banking sector is undergoing the most significant cybersecurity overhaul in its history. The State Bank of Pakistan’s Cyber Shield strategy, a five-year roadmap running from 2025 to 2030, does not just set guidelines. It redefines the rules of engagement for every bank, digital bank, microfinance institution, fintech, and payment service provider operating in the country
Saudi Arabia’s PDPL: Securing the Kingdom Data
Saudi Arabia’s Personal Data Protection Law (PDPL) is not just another compliance requirement — it is a clear signal that the Kingdom is strengthening its data governance landscape in line with global standards.
At Kinverg, we view PDPL as more than a regulatory obligation — it is an opportunity to build trust, enhance reputation, and strengthen competitive positioning in the Saudi market.
ISO 42001 VS EU AI ACT
As organizations expand across cloud environments, remote workforces, and third-party integrations, their attack surface grows faster than their ability to defend it. In this environment, assuming your defenses work is not a strategy — it is a liability. Penetration testing helps organizations move from presumed security to proven security by validating weaknesses before attackers can exploit them.
The Invisible Breach: Why Penetration Testing Is No Longer Optional
As organizations expand across cloud environments, remote workforces, and third-party integrations, their attack surface grows faster than their ability to defend it. In this environment, assuming your defenses work is not a strategy — it is a liability. Penetration testing helps organizations move from presumed security to proven security by validating weaknesses before attackers can exploit them.