ISO 27001 in APAC: A Framework for Cyber Resilience, Not a Breach Proof Badge
Cybersecurity teams across Asia-Pacific face a practical challenge: deciding which risks to address first, who owns them and how to check whether defenses are working. ISO 27001 offers a structured approach through an information security management system (ISMS). Its potential value is better-organized risk management not a promise that certification will prevent every incident.
The risks APAC organizations want to manage
In a 2022 survey of companies across APAC, 70% of respondents cited data loss as a concern about cyberattacks; 58% cited business interruption, 50% reputational damage, 49% theft of intellectual property, 44% costs incurred, 35% ransom payments and 29% regulatory fines.
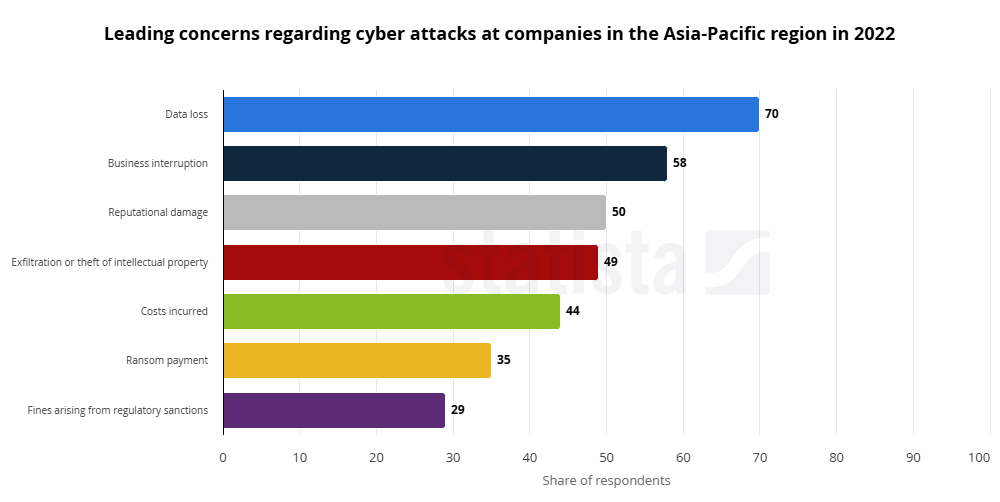
An ISO 27001 program can turn those concerns into a repeatable cycle: assess risks → assign owners → select controls → test and improve. For example, an organization might prioritize access management and backups for sensitive data, then test its incident-response and recovery processes. Those are examples of how a risk-based program can work, not findings that the survey measured.
The threat landscape makes continuous improvement important
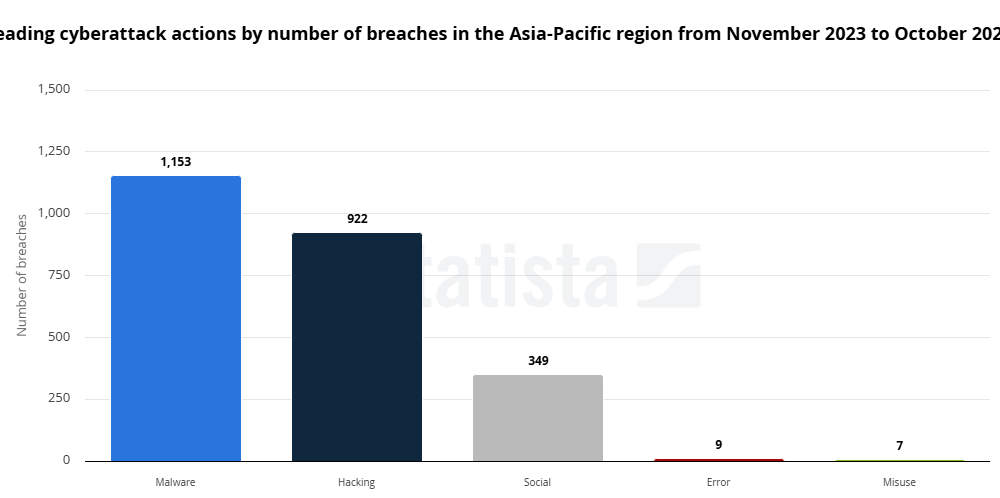
Another APAC dataset counts 1,153 breaches involving malware, 922 involving hacking, 349 involving social actions, 9 involving errors and 7 involving misuse between November 2023 and October 2024.
For APAC businesses, the case for ISO 27001 is therefore operational: it gives teams a way to make security decisions systematic, document accountability and revisit controls as risks change. Certification alone should not be confused with proof of fewer breaches.
What the data does—and does not—show
The cited APAC figures establish what surveyed companies worried about and which actions appeared in recorded breaches. They do not compare ISO 27001-compliant organizations with non-compliant ones, so they cannot establish a percentage reduction in incidents, financial losses or downtime attributable to compliance. The clearest conclusion is that ISO 27001 provides a framework for managing the kinds of risks visible in APAC data; its measurable impact depends on how an organization implements and maintains that framework.
Take the Next Step Towards Stronger Information Security with Kinverg
ISO 27001 is more than a certification. It is a strategic framework that helps organizations protect sensitive information, manage risks effectively, and build trust with customers, partners, and stakeholders. By implementing a robust Information Security Management System (ISMS), businesses can strengthen their security posture while demonstrating compliance with internationally recognized standards. ISO 27001 emphasizes risk management, continuous improvement, and information security best practices.
At kinverg, we help organizations navigate the complexities of ISO 27001 implementation and certification. Our information security experts work closely with your team to assess current practices, identify gaps, establish effective security controls, and prepare your organization for successful certification.
Whether you are beginning your ISO 27001 journey or looking to improve an existing ISMS, Kinverg provides the guidance, expertise, and practical support needed to achieve and maintain compliance.
Contact Kinverg today to schedule a consultation and start your ISO 27001 compliance journey.